Articles

Articles

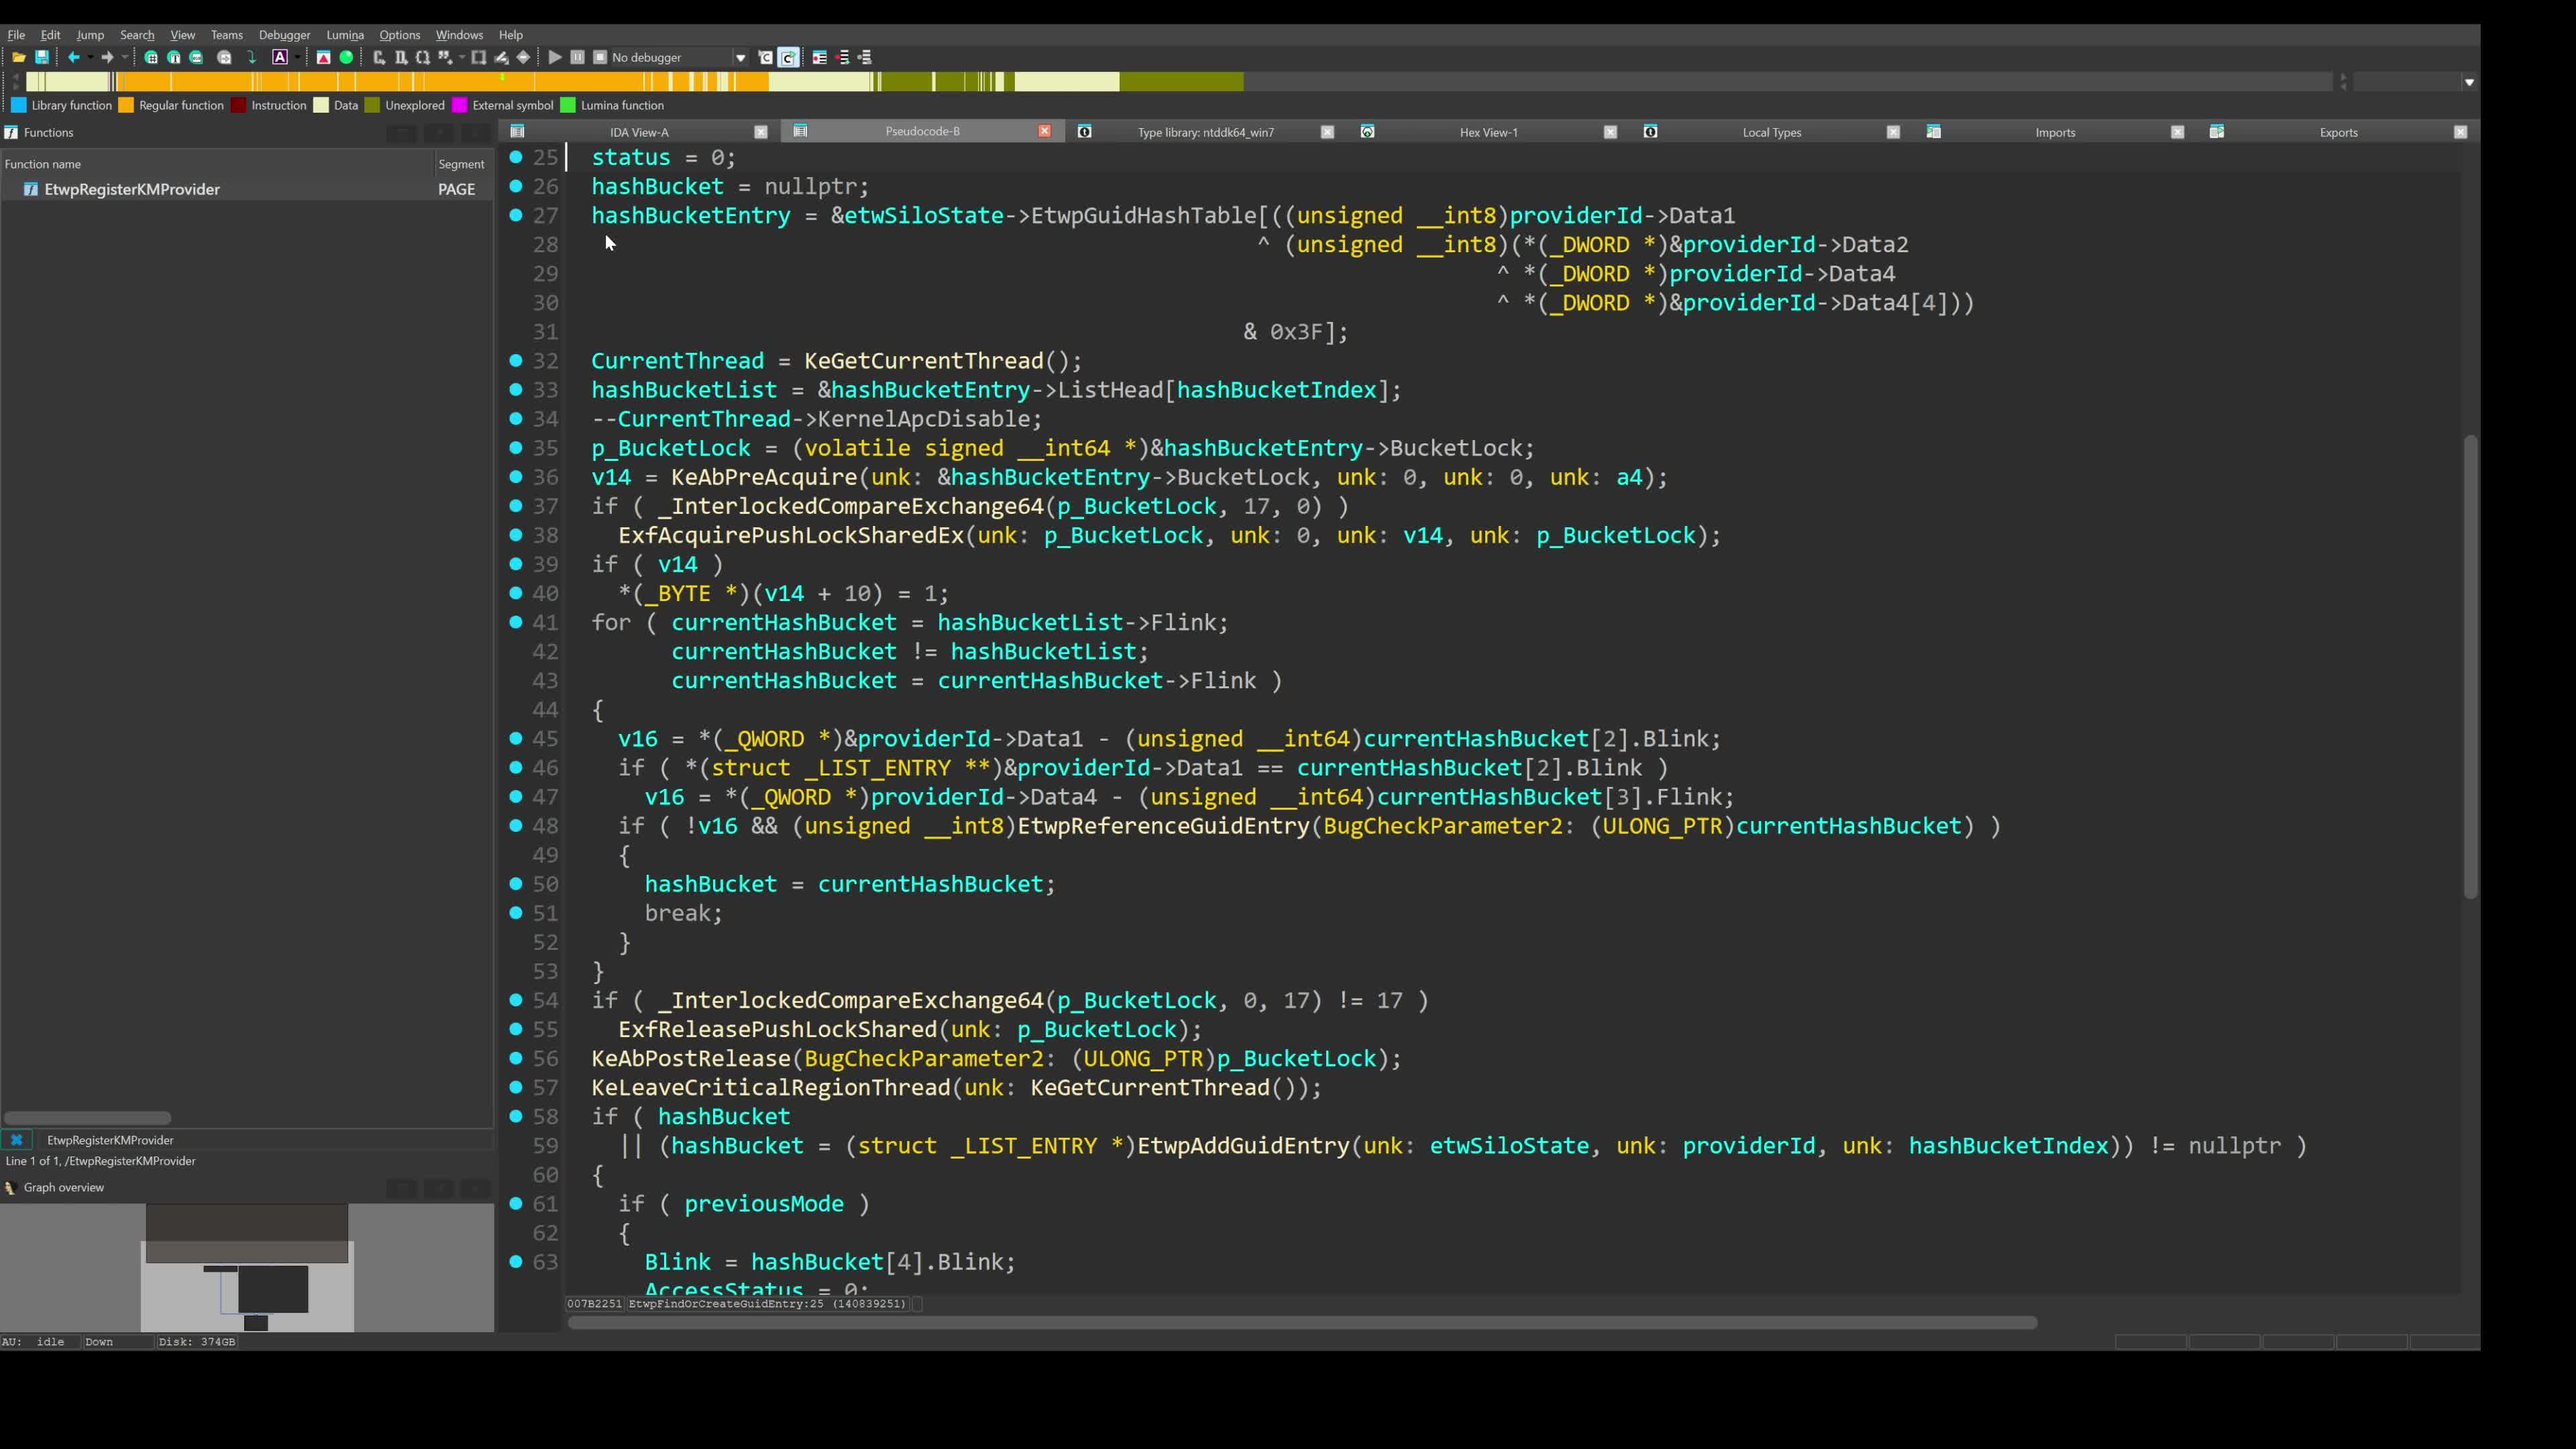
Paint It Blue: Reversing Win32k's Callbacks
28 Sept 2026

Paint It Blue: Reversing Win32k's Callbacks

A reverse-engineering tour of modern Win32k architecture, x64 syscall dispatch, GUI-thread conversion, and the session-aware callbacks behind GDI batching and other executive callouts.

Read more →
EtwSuite video thumbnail
09 Aug 2026

Inside Event Tracing for Windows with EtwSuite

Event Tracing for Windows is one of Windows' richest telemetry systems. This video introduces the ETW ecosystem and shows how EtwSuite can turn raw provider events into practical security research and UAC-bypass detections.

Read more →
hypervisor-based-defense
14 Mar 2026

Hypervisor Based Defense

Hey there, it has been a "little" while since I published my last post. After scrapping and rewriting multiple ideas, I decided to write something a bit different from my previous posts. This post contains technical information, but I also wanted to share my thoughts after working on a hypervisor project for more than a year.

Read more →
lotr06
31 Mar 2024

Lord Of The Ring0 — Part 6 | Conclusion

In the last blog post, we learned about two common hooking methods (IRP Hooking and SSDT Hooking) and two different injection techniques from the kernel to the user mode for both shellcode and DLL (APC and CreateThread) with code snippets and examples from Nidhogg. In this blog post, we will write a simple driver that is capable of bypassing AMSI to demonstrate patching usermode memory from the kernel, go through credential dumping process from the kernel and finish with tampering various kernel callbacks as an example for patching kernel mode memory and last but not least - the final words and conclusion of this series. In the last blog post, we learned about process hiding and got into the internals of some of the most dangerous patching methods from the kernel.

Read more →
lotr05
19 Jul 2023

Lord Of The Ring0 — Part 5 | Saruman's Manipulation

In the last blog post, we learned about the different types of kernel callbacks and created our registry protector driver. In this blog post, I'll explain two common hooking methods (IRP Hooking and SSDT Hooking) and two different injection techniques from the kernel to the user mode for both shellcode and DLL (APC and CreateThread) with code snippets and examples from Nidhogg. While there are couple of methods to perform operations from kernel mode on user mode processes, in this part I will focus on one of the most common methods that allow it with ease - KeStackAttachProcess.

Read more →
lotr04
24 Feb 2023

Lord Of The Ring0 — Part 4 | The Call Back Home

In the last blog post, we learned some debugging concepts, understood what is IOCTL how to handle it and started to learn how to validate the data that we get from the user mode - data that cannot be trusted and a handling mistake can cause a blue screen of death. In this blog post, I'll explain the different types of callbacks and we will write another driver to protect registry keys. We started to talk about this subject in the 2nd part, so if you haven't read it yet read it here and come back as this blog is based on the knowledge you have learned in the previous ones.

Read more →